Talk with our engineers by joining the new Onehouse community Slack!
Ecosystem and integrations
Security and governance
Onehouse signs users in through your identity provider, controls access to platform resources and to data separately, and can leave every credential in your own secret manager.
Authentication. Single sign-on through your identity provider, including Okta, Google, Microsoft Entra, and any SAML provider, is on by default, and you can restrict sign-in to one provider. SCIM 2.0 provisioning from Microsoft Entra syncs users and groups one way, from your identity provider into Onehouse. Service principals issue tokens for programmatic access.
Authorization has two halves. Roles apply to Onehouse resources (accounts, projects, groups, service principals, clusters, sources, catalogs, flows, jobs), generally as Viewer, User, Editor, and Manager. Privileges apply to data objects (lakes, databases, tables) and propagate downward, so a privilege on a lake reaches every current and future database beneath it. Data privileges live in the Onehouse governance catalog, which enforces them on every query, down to row filters.
Project membership and resource access are separate. An invited user is a member of the project but sees nothing until granted roles on individual resources.
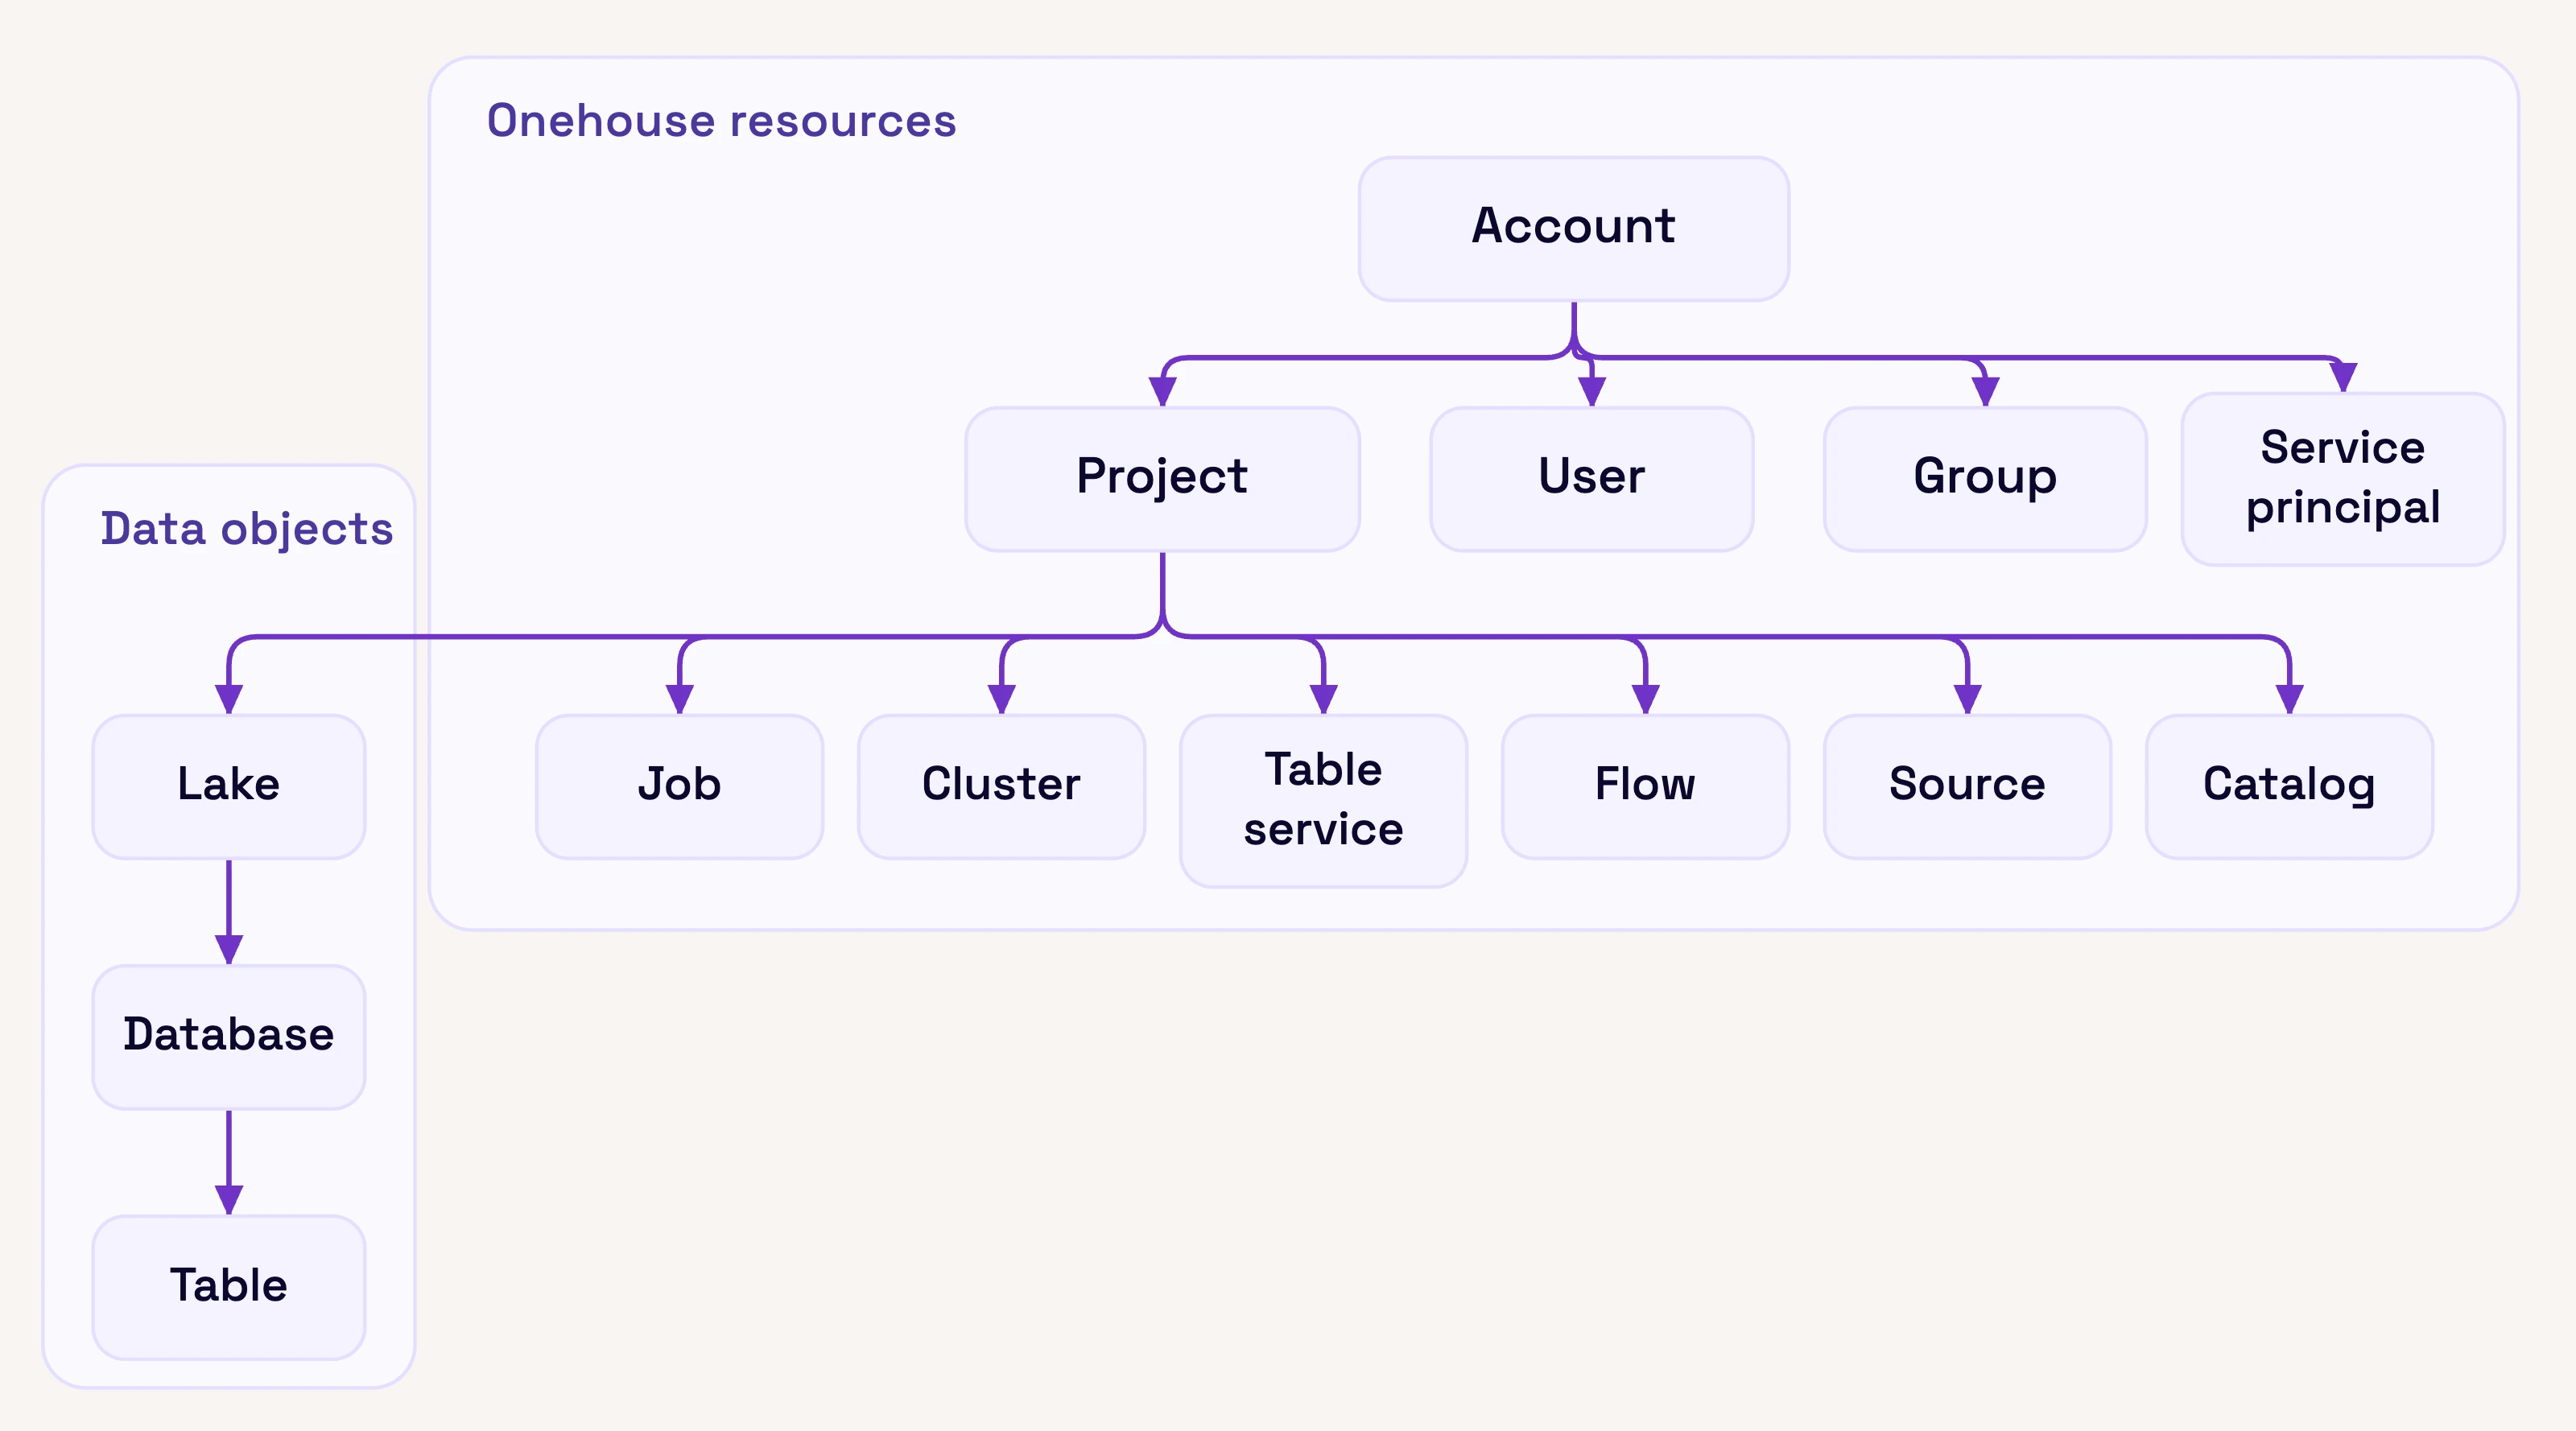
Onehouse resources take roles. Data objects take privileges, which propagate from lake to database to table.
Agent access. The AI Gateway controls which users and groups can call each model and use each tool, and brokers provider credentials so no agent holds a key. Data access for agents goes through Lakegres, which enforces the same governance catalog policies as every other query.
Secrets are held either as Onehouse-managed secrets or under bring-your-own-secrets, where the credential stays in your secret manager and Onehouse holds only a reference. Onehouse reads only the secrets you explicitly opt in, by tag on AWS or by name prefix on Google Cloud. Bring-your-own-secrets is set at deployment time and is the recommended configuration.
Compliance. Onehouse is SOC 2 Type I and Type II certified and holds PCI DSS certification. Tables are held in open formats in your own storage, so other tools can still read your data if you remove the platform. The table format supports record-level deletion for regulations such as GDPR.